
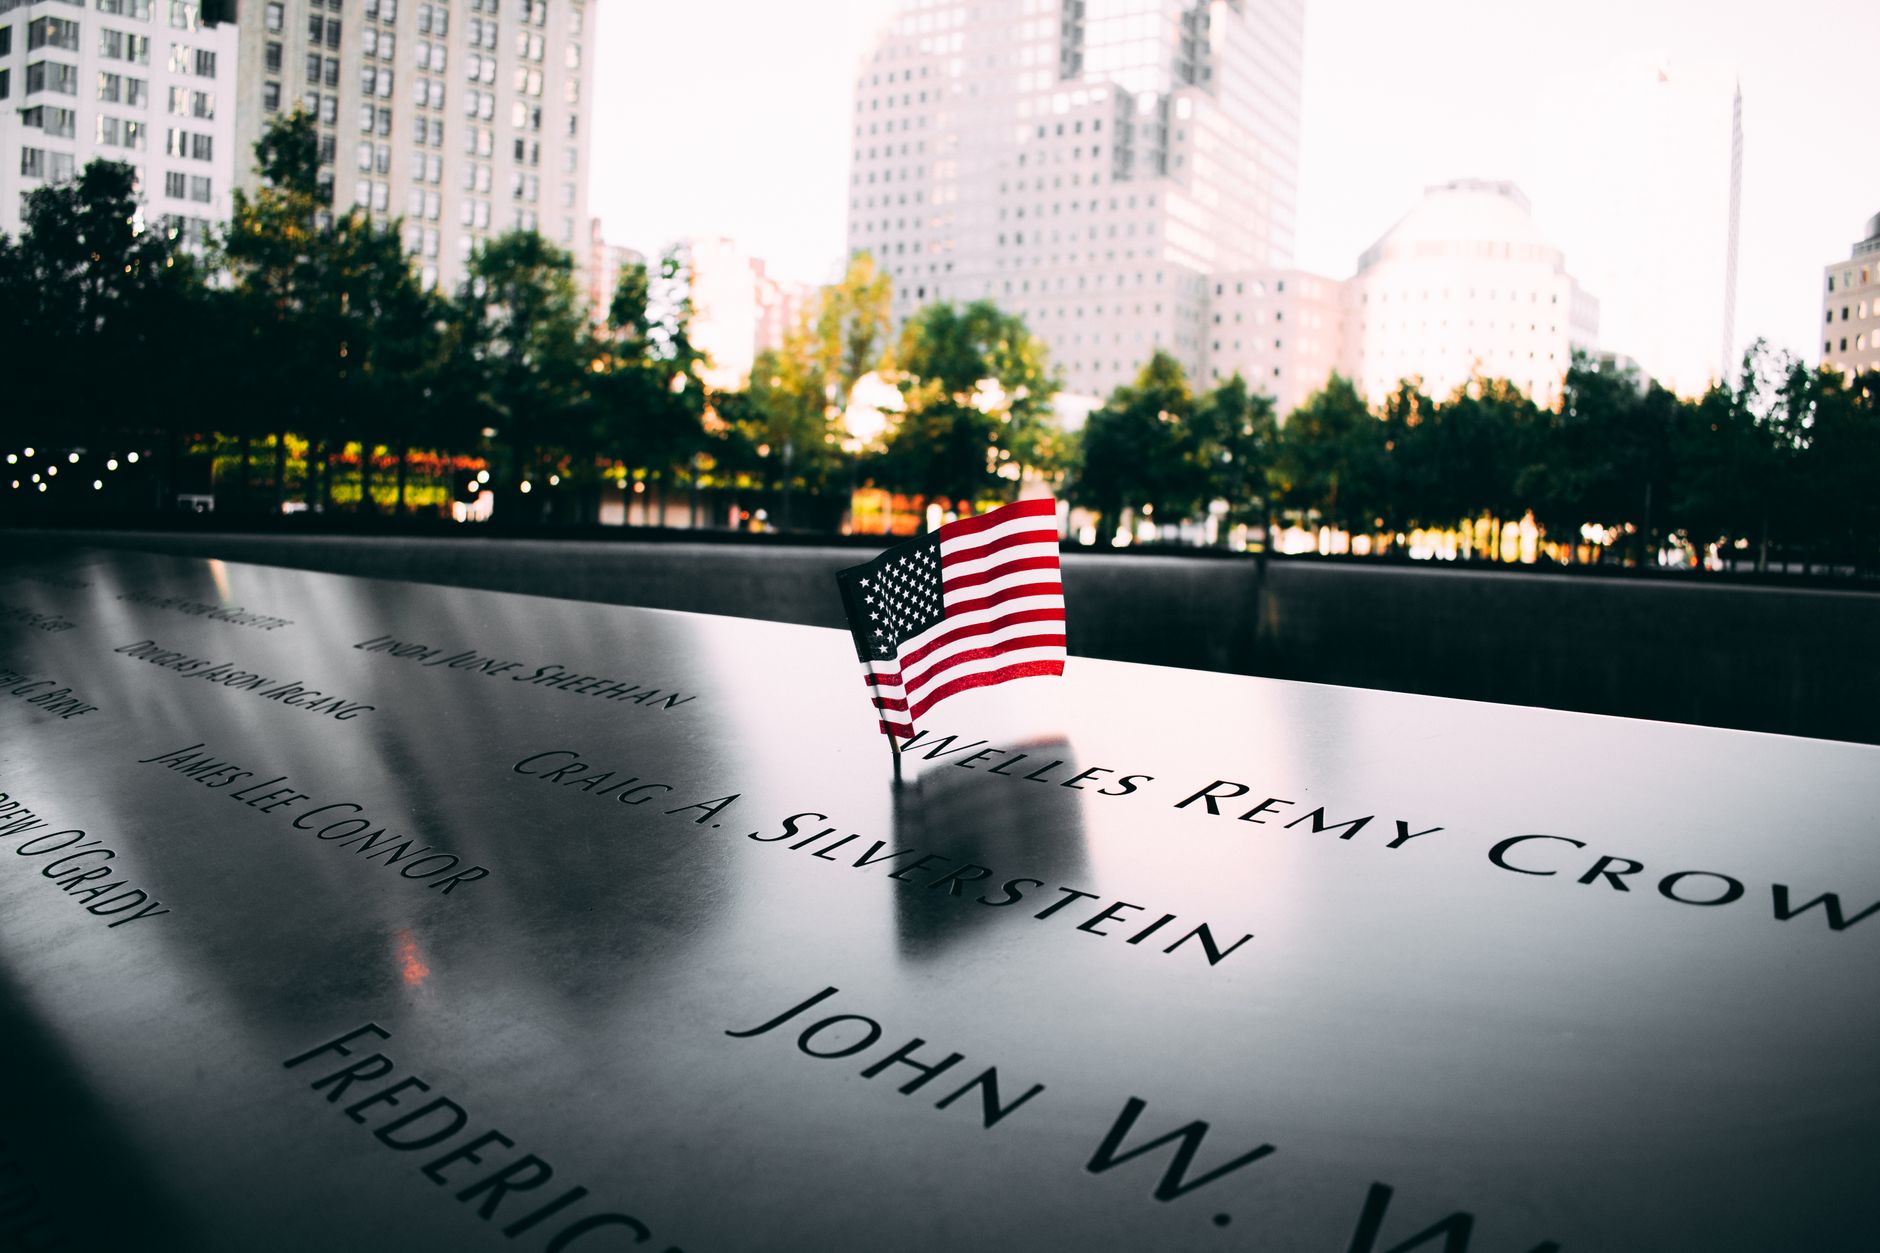
When the towers fell on a September morning in 2001, the shockwaves rippled far beyond the immediate tragedy. In the months that followed, a quiet but profound transformation began in the United States: the government started to watch its own citizens with a vigor that would have seemed unthinkable just weeks earlier. This isn’t a story about conspiracy theories; it’s a chronicle of policy, technology, and the uneasy balance between safety and liberty that still defines America today.
What's Going On
In the immediate aftermath of the attacks, lawmakers rushed to pass legislation that would give intelligence agencies the tools they needed to prevent another catastrophe. The most famous of those tools was the USA PATRIOT Act, which broadened the scope of wiretaps, data collection, and information sharing across agencies. As the legal framework expanded, so did the technical capabilities that could exploit it. According to How 9/11 Changed the Way America Surveil, the federal government began to leverage emerging digital infrastructures—cell towers, internet backbone, and even commercial databases—to build a surveillance ecosystem that could track, analyze, and predict behavior on a massive scale.
The early 2000s saw the rise of metadata collection, where phone call logs, email headers, and even travel records were harvested en masse. The National Security Agency (NSA) famously tapped into undersea fiber‑optic cables, while the Department of Homeland Security created the “Fusion Center” model to aggregate data from local, state, and federal sources. The goal was simple: create a “big picture” view of potential threats before they could materialize.
Technology, however, moved faster than any legislative oversight. The proliferation of smartphones, social media platforms, and cloud services gave agencies unprecedented access points. By the time the Snowden revelations hit in 2013, it became clear that the surveillance state had grown into an intricate web of partnerships with private corporations, data brokers, and even foreign allies. The public debate shifted from “Can we prevent another 9/11?” to “How much of our private lives are being cataloged without our consent?”
Why This Matters
The ripple effects of this surveillance expansion touch every corner of the tech industry. Companies that once sold hardware now find themselves building software pipelines designed to comply with government data requests. As General : Fahmi Urges Parents To Make Us highlighted, the push for digital controls in one part of the world mirrors a broader global trend: governments demanding backdoors, encryption weakening, and a growing expectation that tech firms act as de‑facto surveillance agents.
From a civil liberties perspective, the stakes are equally high. The Fourth Amendment was written for a world of paper records, not for algorithms that can predict a person’s next move based on a handful of data points. Legal scholars argue that the lack of clear oversight mechanisms creates a “gray zone” where agencies can operate with minimal accountability. This has led to a surge in advocacy groups filing lawsuits, demanding transparency reports, and lobbying for stronger privacy legislation.
Businesses that rely on consumer trust—especially those in fintech, health tech, and e‑commerce—must now navigate a landscape where data collection is both a regulatory requirement and a potential liability. A breach of trust can mean not just lost customers, but also intense scrutiny from agencies that already have a foothold in the data ecosystem.
What It Means for the Industry
For technology providers, the post‑9/11 surveillance model has become a double‑edged sword. On one hand, contracts with intelligence agencies have funded research into advanced analytics, machine learning, and real‑time data processing. On the other, the same capabilities can be weaponized against competitors or used to stifle innovation under the guise of national security. Companies now embed “privacy by design” principles not only to appease regulators but also to differentiate themselves in a market where consumers are increasingly savvy about data rights.
Strategically, firms are investing in encryption technologies that balance government access requests with user privacy. Zero‑knowledge proof systems, homomorphic encryption, and secure multi‑party computation are no longer academic curiosities; they are becoming essential components of product roadmaps. Meanwhile, the rise of “edge computing” allows data to be processed locally on devices, reducing the need to transmit raw information to central servers—a subtle but powerful way to limit mass collection.
Another trend is the emergence of “surveillance‑resistant” platforms that deliberately avoid centralized data storage. Decentralized social networks, peer‑to‑peer messaging apps, and blockchain‑based identity solutions are gaining traction among privacy‑focused users. However, these alternatives also face pressure from regulators who argue that they can be used to evade lawful investigations.
Amid this tug‑of‑war, the industry must also reckon with the ethical implications of predictive policing, facial recognition, and AI‑driven threat assessment. The technology that can spot a suspicious pattern in a sea of data can just as easily reinforce bias, leading to disproportionate scrutiny of certain communities. Companies that ignore these concerns risk not just legal penalties but also reputational damage that can be far more costly.
Even the fourth mandatory link finds its place here: the conversation around digital safeguards is not limited to the United States. As General : Safeguard Malaysiaâ€TMs Democ noted, nations worldwide are grappling with the same balance of security and liberty, and the solutions they adopt will inevitably influence global tech standards.
What Happens Next
Looking ahead, the surveillance landscape is set to become even more intricate. The rollout of 5G networks will dramatically increase the volume and velocity of data, giving agencies finer‑grained location tracking and the ability to intercept communications with near‑zero latency. Simultaneously, advances in quantum computing threaten to render current encryption methods obsolete, prompting a race to develop quantum‑resistant algorithms.
Legislatively, Congress is expected to revisit the PATRIOT Act’s provisions, especially around bulk data collection and “Section 702” of the FISA Amendments. The debate will likely center on whether to tighten oversight or expand powers in the name of counter‑terrorism. Meanwhile, state‑level privacy laws—like California’s CCPA and Virginia’s CDPA—are pushing the federal government to adopt a more uniform privacy framework.
For tech leaders, staying ahead means embracing transparency, investing in privacy‑enhancing technologies, and engaging in policy discussions before regulations force reactive changes. The full announcement of upcoming reforms can be found in the detailed analysis by I asked ChatGPT and Gemini to build a mo, which outlines potential scenarios for the next decade.
Ultimately, the story that began on a tragic September day is still being written. The tools that protect us can also erode the very freedoms they aim to safeguard. As citizens, technologists, and policymakers, our challenge is to shape a future where security and privacy coexist, rather than compete.


